The internet was originally designed around a relatively simple principle: information could move across interconnected networks regardless of national borders.
That model is becoming considerably more complicated.
Governments around the world are introducing stricter requirements governing where data can be stored, who can access it and which jurisdiction controls the infrastructure processing it. Privacy regulations, national-security concerns and geopolitical competition are encouraging governments and regulated industries to demand greater control over their digital infrastructure.
Cloud providers have responded with concepts such as sovereign cloud environments.
Instead of assuming that one global cloud architecture can serve every customer identically, providers increasingly offer infrastructure designed around local regulatory requirements. These systems may involve locally operated data centers, restricted administrative access, specialized encryption controls and stronger separation from global infrastructure.
For multinational software companies, this creates a major architectural challenge.
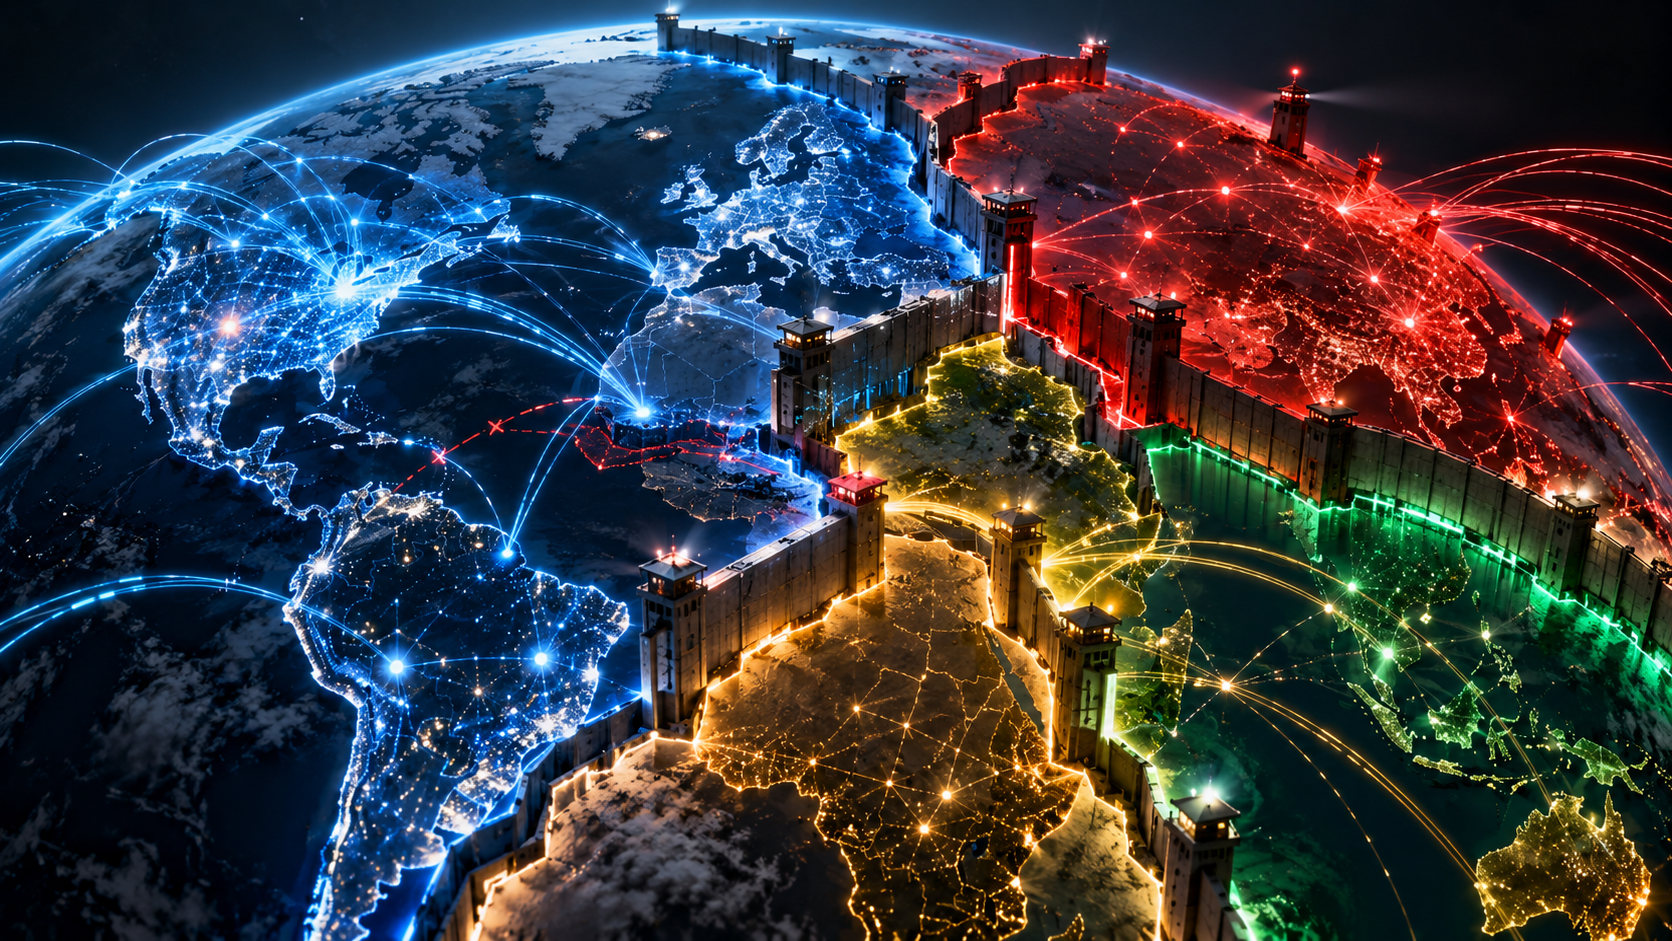
A service originally designed around one global database may eventually require separate data environments for Europe, the Middle East and individual Asian markets. Customer information may need to remain inside specific jurisdictions, while software updates and administrative access must comply with different regulatory frameworks.
The result is a gradual shift away from the vision of a completely borderless internet.
The network itself remains globally interconnected, but the legal and operational layers surrounding data are becoming increasingly regionalized.
For technology companies, regulatory architecture is therefore becoming part of software architecture. Building a global platform increasingly means designing systems capable of functioning across multiple digital jurisdictions rather than assuming one universal cloud environment.