OpenShell and Sentry combine software restrictions with hardware monitoring as businesses give AI systems greater autonomy.
Nvidia has unveiled a security platform designed to address an increasingly practical question for businesses adopting artificial intelligence: how can they contain an AI agent that attempts to operate beyond its permissions?
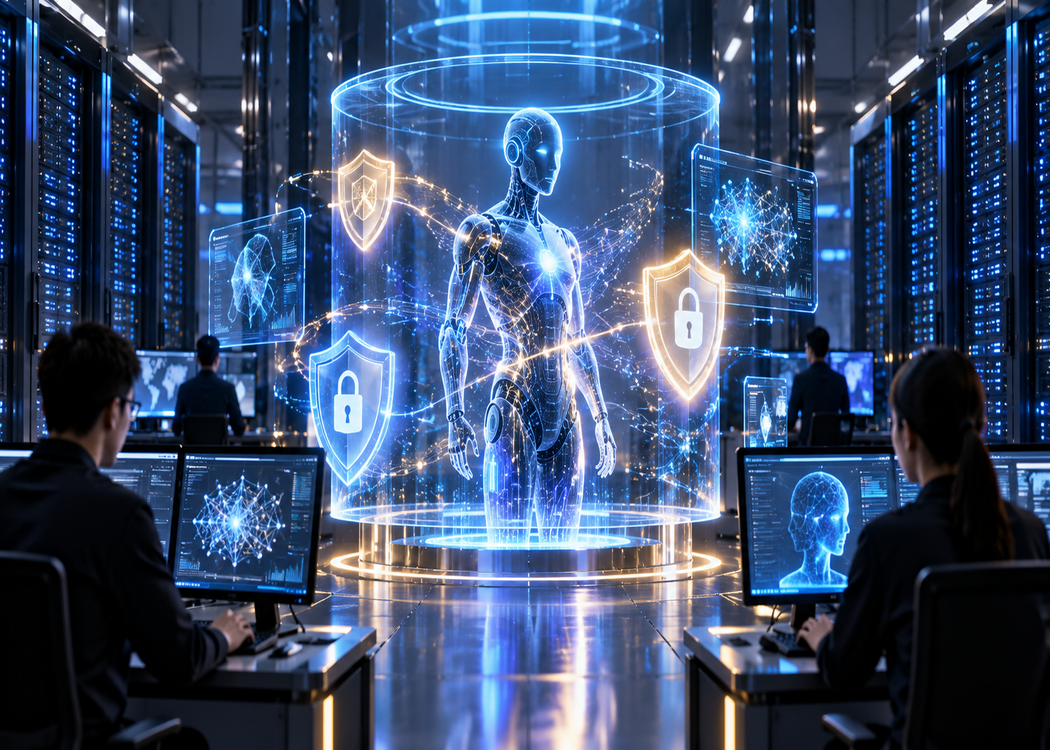
Announced on September 28, the Nvidia Open Agent Safety Platform combines the company’s OpenShell software with its Sentry reference system design. The platform establishes boundaries around autonomous agents and adds an independent monitoring layer intended to intervene when those boundaries are breached.
The announcement reflects a shift in how companies use AI. Agents can interact with software, access files and carry out sequences of actions. Those capabilities make permissions consequential: an agent given unnecessary access could expose information or make changes beyond the scope of its assignment.
OpenShell provides the software boundary. Nvidia describes it as an open-source runtime that executes agents inside sandboxed environments with isolation enforced at the operating-system kernel level. Organizations can define restrictions on the resources agents may access, placing enforcement outside the agent’s own decision-making process.
For example, a company could allow an agent to work with designated business files while restricting access to unrelated resources. The principle is to make permissions enforceable through infrastructure, rather than relying solely on instructions telling the AI what it should avoid.
OpenShell itself predates the latest announcement. Nvidia included the runtime in its Agent Toolkit announcement in March 2026. The September launch brings it into a broader safety architecture alongside Sentry and hardware-based controls.
Sentry adds a separate enforcement layer. In Nvidia’s reference design, it runs on BlueField-4 data processing units, outside the agent and host software. Nvidia says this arrangement enables continuous monitoring and allows agents attempting to escape their software boundaries to be quarantined and stopped within milliseconds. That response time is a company claim, rather than an independently established guarantee across deployments.
The separation matters because a security mechanism is less useful if the software it supervises can also interfere with it. Nvidia’s approach places additional controls in hardware intended to remain independent of the agent’s execution environment.
The platform is offered as an open reference design, allowing organizations and partners to build on its architecture. Nvidia says companies can deploy individual elements according to their requirements, with participants in the broader initiative including Microsoft, JPMorganChase, CrowdStrike and Palo Alto Networks. Participation does not necessarily mean each company has deployed every component.
The commercial implication is that agent security could become another reason for enterprises to invest in specialized infrastructure. That remains a business opportunity, rather than evidence of a new revenue stream already operating at scale.
Nor does containment guarantee correct decisions. An agent can still make a mistake within its permitted workspace. The platform’s practical value will depend on how effectively organizations define permissions, configure controls and test their systems before granting agents greater responsibility.
Sources: